3.3.10. Memory Image
3.3.10.1. What is it
Allows you to import a memory image and use open source tools to process it.
Cyber Triage will not make an image of memory.
Cyber Triage uses two open source tools to parse Windows memory images:
Note
Linux memory images are not supported.
Supported memory image formats:
Raw (.img, .bin, .raw, .mem)
Lime (.lime)
AFF4 (.aff4)
.dmp
.vmem
.hpak
.E01
Note
A host created from a memory image will not have all of the data and fields that you’d see from the Cyber Triage® Collector. The interface will identify places that have incomplete data.
Watch the Cyber Triage Basics Course Memory video on this technique.
3.3.10.2. How to Get The Data
Use any memory imaging tool.
3.3.10.3. Where To Put Your Data
The following locations are supported based on your access method:
Application |
Supported Locations |
|---|---|
Standard |
Locally accessible |
Team, Web Client |
Server Accessible Folder. |
Team, Local Client |
Locally Accessible or Server Accessible Folder |
If you are using the Team with a local client and the data is locally stored, then the client will do the parsing of the image and send the results to the server. The client must continue to run until the parsing is complete.
3.3.10.4. How to Import
To add Memory Image data, choose Add New Host from the Incident Overview and choose the Memory Image box.
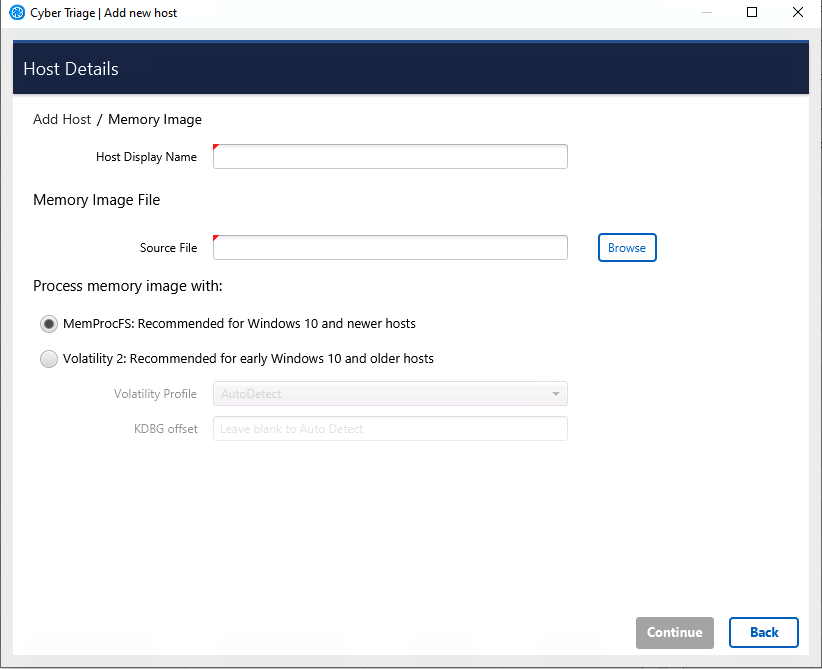
Browse to your memory image file.
Choose what tool you’d like to use. MemProcFS has more complete support for Windows 10 and newer.
If you choose Volatility 2, you can also specify a profile and KDBG offset if auto detection is not working.
Update the display name and reference date as needed.
Press Continue to then configure what data types to collect (see Specifying Data Collection Types) and malware settings (see Ingest-Time Settings).